Hacker steals $106M from EU entity’s CEX accounts on Nov 1
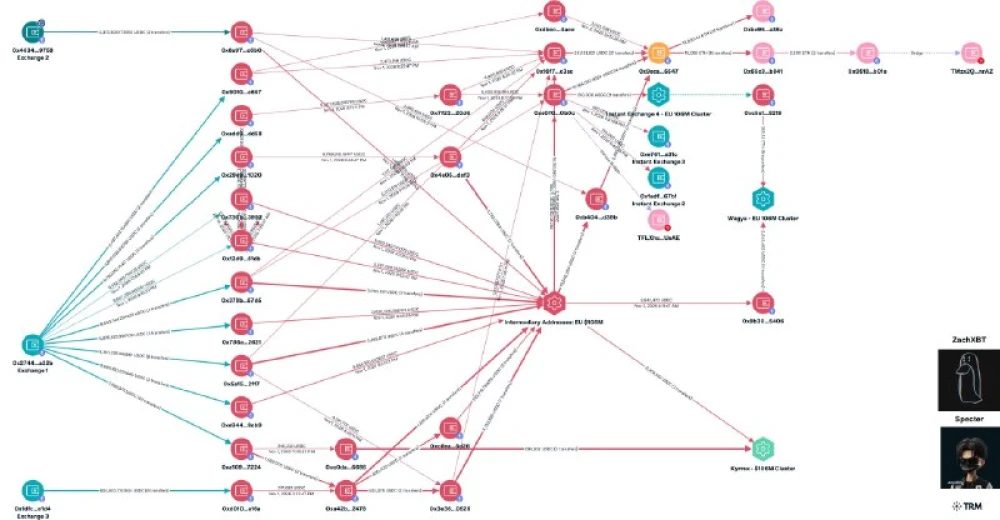
An EU entity is suspected to have lost more than $106 million from multiple centralized exchange accounts on Nov 1. The illicit actor withdrew funds as USDC and USDT and began obfuscating flows shortly after.
Observed fund flows
- Swapped USDC to ETH at scale.
- Sent assets to instant exchanges including WellWallet and Kyrrex.
- Converted portions to XMR through Wagyu.
- Bridged assets across multiple chains to disperse exposure.
Known theft addresses
- 0xADd95cD98E0288ba69785E3151E1db86adF8Dd58
- 0x29e9D7715D935e0D0D4B0DD0efC952A97E551020
- 0x378B4f150707C283574DC89739608D29036D57d5
- 0x795a9d22F233024487161Fe6daFf73397c162621
- 0x730Bcb1296758c377149d7409f98f041cf723992
- 0x12D9012731eb0D54871A31Af5566Eb9ECCa351Db
- 0x5A154f77852ed274Fd6F4c324a1Ee27809052FF7
- 0xA1096A66f9ed58A9594A6A1ad67A5472C0907224
- 0x90F0b6D51ed2FE2348A45b2C49BC441E959bc557
- 0x8A97BC406180e28b11C5495fA099BF5119c6C6B0
- 0xd010cba790a6ab0048da18f2fbe8e3faf463a16a
Key facts
- Date: Nov 1
- Estimated loss: $106 million plus
- Initial assets: USDC and USDT
- Subsequent assets and routes: ETH swaps, XMR conversions through Wagyu, transfers via instant exchanges, and multi-chain bridging
Authors credited by the source: investigations
Published by Holder based on an external source.