Attackers stole Binance deployment token via employee PCs
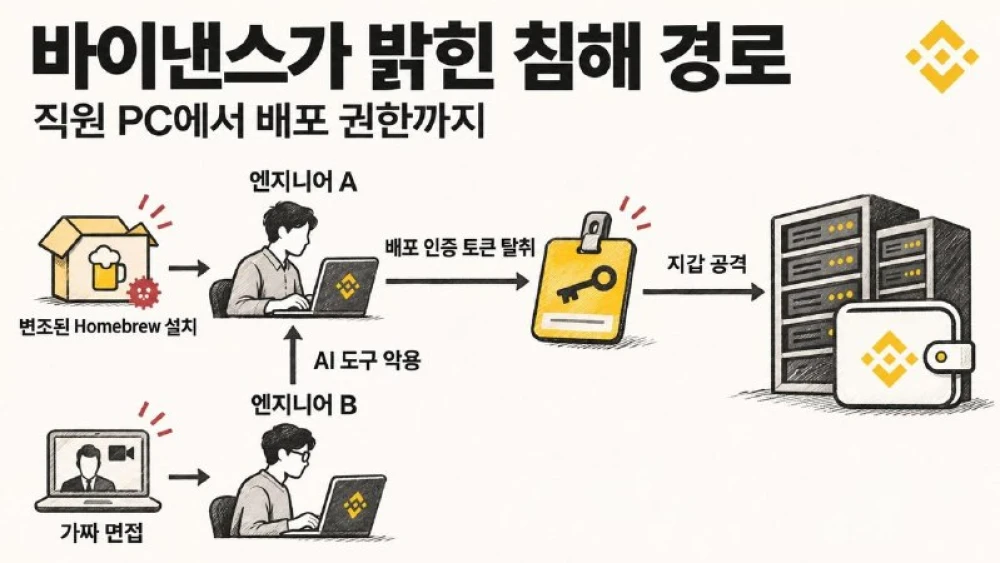
In the Binance hack, the attackers went from employee PCs all the way to deployment privileges.
According to Binance’s account relayed by AggrNews, two employees’ PCs were compromised via different vectors.
- Engineer A: infected through a tampered Homebrew installation process. Homebrew is a program used on Mac to install development tools, etc.
- Engineer B: infected via a fake job interview. The attacker allegedly abused an AI tool on B’s PC to gain access to A.
- They then used a deployment authentication token stolen from A for a wallet attack.
This should be read not as AI hacking on its own, but as the attacker abusing tools and privileges on employees’ PCs.
Individuals should also be cautious if someone sends installers or execution commands under the pretext of an interview or collaboration. If you keep trading keys or important logins in your AI work environment, a breach in one place can spill over to the other. Even if you separate devices, sharing credentials weakens the separation effect.
Authors credited by the source: c4lvinlocked
Published by Holder based on an external source.